NVIDIA's OpenShell blueprint puts AI agents in a box, with a chip that can stop them in milliseconds
At GTC Berlin, NVIDIA unveiled the OpenShell Reference Architecture, a hardware-and-software design for running AI agents safely. Anthropic, OpenAI, Google Cloud, Microsoft and Meta are among those working with it.
By ScoviAI Team
Key points
- Announced at GTC Berlin on October 21, 2026
- Combines Vera Rubin servers for models, Vera CPUs for agents and BlueField-4 chips that police agent behavior
- NVIDIA says its Sentry software can quarantine an agent that steps out of bounds in milliseconds
- Anthropic, OpenAI, Google Cloud, Microsoft, Meta, SAP and the banks BBVA and Santander are involved
AI agents that can click, type and run code inside a company's systems are useful. They are also a new kind of security risk. At GTC Berlin, NVIDIA presented its answer: build the guardrails into the hardware.
The NVIDIA OpenShell Reference Architecture is a blueprint for "building, containing, observing and enforcing safe agents" on company servers and on edge devices.
"As enterprises prepare to deploy billions of AI agents, safety and control must be built into the computing architecture." Jensen Huang, NVIDIA founder and CEO
What's in the OpenShell blueprint?
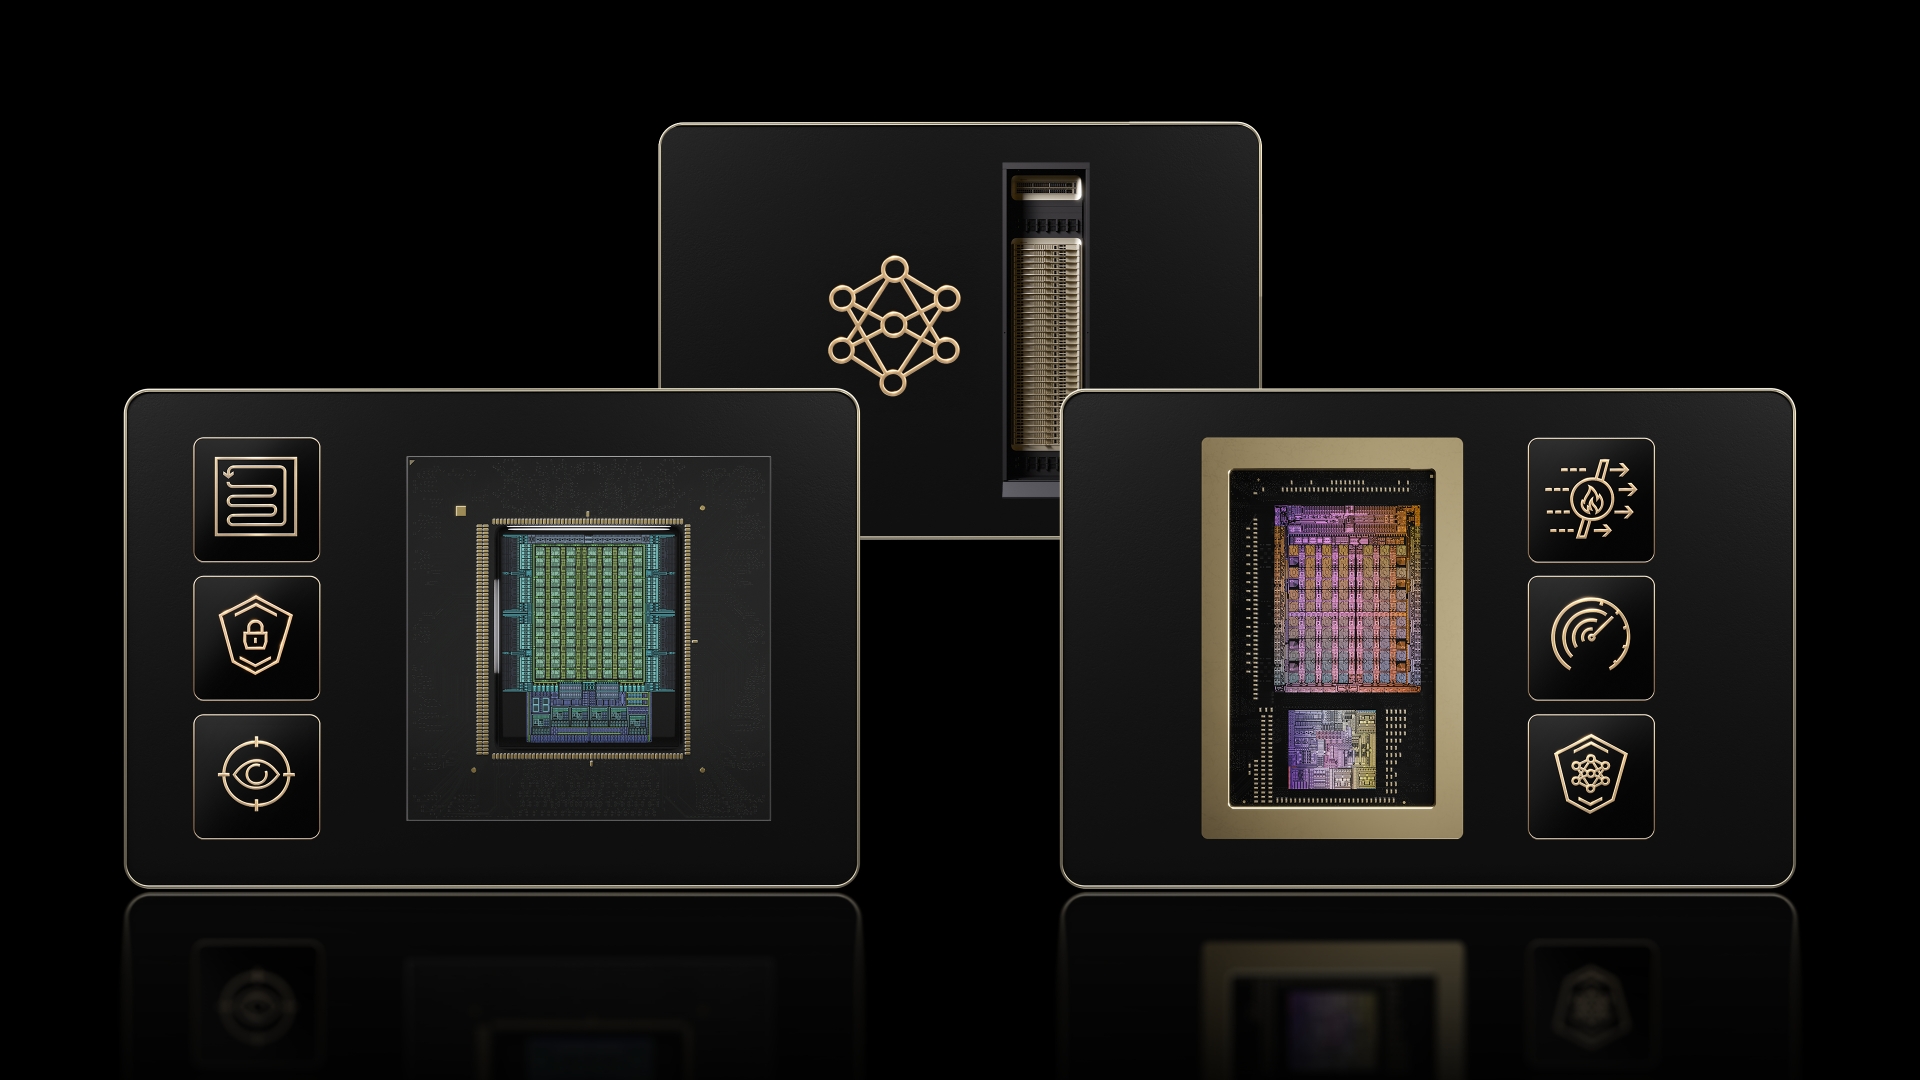
Huang summed it up as agents that "think on Rubin, act on Vera and be governed on BlueField." In plainer terms, each part of the job runs on a different piece of hardware:
| Part | What it does |
|---|---|
| Vera Rubin servers | Run the AI models, closed or open |
| Vera CPUs | Run the agent itself, including its tools, inside OpenShell's secure runtime |
| BlueField-4 DPUs with NVIDIA Sentry | Watch what the agent does and enforce the rules in the chip |
The key piece is Sentry. It monitors agent behavior "out of band," meaning separately from the agent's own software. NVIDIA says that if an agent tries to step outside its allowed boundary, Sentry quarantines and stops it in milliseconds. Because the check happens in silicon, a compromised agent can't simply switch it off.
The design also extends to smaller machines at the edge, such as NVIDIA's RTX Spark laptops and DGX Spark and DGX Station systems, for uses in retail, healthcare, factories, robotics and telecoms.
Who is working with OpenShell?
NVIDIA's list is long. Among the companies it names:
ADVERTISEMENT
- Model makers: Anthropic, Cohere, Google, Meta, OpenAI, Perplexity, Reflection and SpaceX Super Intelligence.
- Clouds and operating systems: AWS, Google Cloud, Microsoft Azure, Canonical, Red Hat, SUSE and Windows, using Microsoft Execution Containers.
- Security firms: 1Password, Check Point, CrowdStrike, Cisco, F5, Fortinet, Okta, Palo Alto Networks and Zscaler, among others.
- Banks: BBVA and Santander are exploring it for agent governance.
SAP is integrating it into its Joule Studio runtime, and ServiceNow announced a long-running personal agent called ServiceNow Arc on the same day.
What we can't verify yet
Performance claims, such as Vera Rubin NVL72 systems delivering "30x higher throughput per megawatt" for agent workloads and Sentry boosting agent capacity by up to 20%, are NVIDIA's own figures. Being on the partner list also doesn't mean a company has deployed the design in production.
Why it matters
Until now, most agent safety has been software rules written by the agent's maker. OpenShell argues the boundary should be enforced by infrastructure the agent can't touch. It's a hardware-maker's view, and conveniently it sells more NVIDIA hardware, but the problem is real. Password managers are tackling the same worry from another angle, as with 1Password for Agents.
Sources
ScoviAI Team is the ScoviAI newsroom. We write every article ourselves from the original announcements and link our sources. Spotted a mistake? Tell us and we'll fix it.
ADVERTISEMENT